When the client calls the firm
Your firm verifies the client
Your adviser asks, “What are the words?” The client reads all three from their Halden Park ID Verify app, and your adviser checks them on the request before acting.
Verification for registered investment advisers
Cloned voices and hijacked inboxes let criminals pass the checks advisers rely on, and the request reaches your team sounding exactly like your client.
Trust Onion puts identity verification in an app branded as your firm. Don’t trust the voice. Verify the client.
Book a security review For security teams: how it’s secured

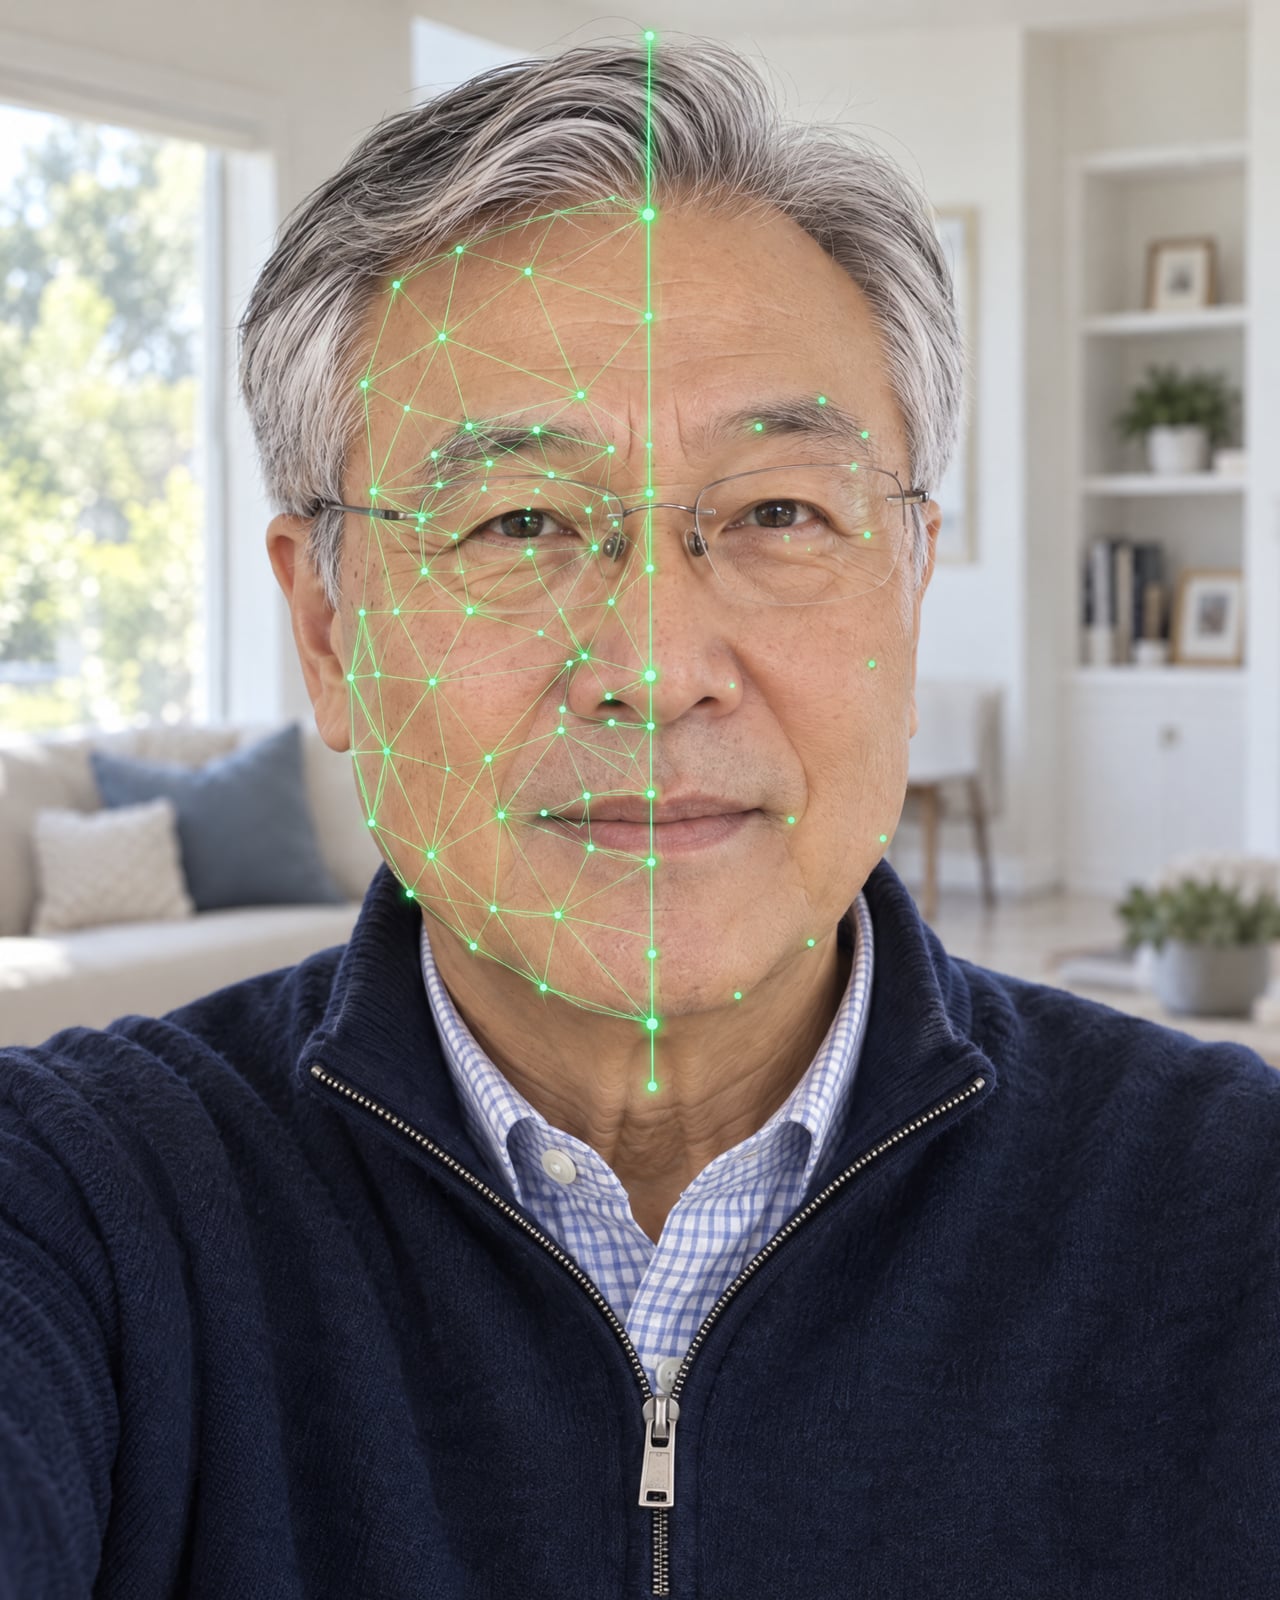
The next call from him might not be him.
The ground shifted
An attacker who controls your client’s inbox and phone number, and has cloned his voice, can pass each check below.
Your firm already confirms requests by email and calls back the number on file. AI adds the voice: a clone built from about 15 seconds of audio, from a voicemail greeting or a family video, can sound like your client. When the number has been moved, your callback reaches the attacker.
A phishing link or a reused password gives the attacker your client’s email. They read years of messages with your firm, then send wiring instructions from his real address.
A SIM swap, a carrier port-out or call forwarding moves the client’s phone number, so caller ID matches and your callback reaches the attacker.
About 15 seconds of audio can be enough to clone a voice, and the answers to security questions sit in breached data and social media.
An urgent wire to a new title company, outside the usual pattern, with his wife left out.
Each device generates the three words locally. They rotate every 60 seconds, out of reach of anyone holding only the inbox and number.
#4127 · $385,000 · Scottsdale condo closing
Henry Cho (phone) · Account: Cho joint brokerage
CHO HOUSEHOLD
Rotates every 60 seconds, generated on this phone
Both directions
Attackers impersonate clients to move money, and they impersonate advisers to get clients to share logins or “move funds to a safe account.” The same three words cover both calls.
The same three live words verify the client calling the firm and the firm calling the client. Family members in the household group also verify each other.
When the client calls the firm
Your adviser asks, “What are the words?” The client reads all three from their Halden Park ID Verify app, and your adviser checks them on the request before acting.
When the firm calls the client
The client asks, “What are the words?” Your adviser reads all three from the firm’s view, and the client checks them in their app before sharing anything.
“Susan, it’s Marcus. We’ve flagged fraud on your account and need to move your funds to a safe account today.” If Marcus can’t give the words, Susan hangs up and calls the number she knows.
Inside the household
Henry and Susan’s daughter Emily is in the same group. When “Emily” calls from a new number asking for money, Henry asks for the words.
The rule never changes: whoever places the call says the words. Whoever answers checks them.
What’s at stake
The cost of one misdirected wire reaches well past the wire itself.

The new standard
Your adviser matches three live words against the request in one question. For doubtful requests, a signed live selfie adds proof, and your dual approval and the custodian’s checks still run before funds move.
The client calls. His device generates three live words in your firm’s app, and the words rotate every 60 seconds.
Your adviser sees the same words. They appear on the request in the firm’s view.
The client confirms. Your adviser asks “What are the words?” and he reads them aloud.
Any doubt, a Proofie™. Your adviser requests a live selfie, signed by his passkey after a Face ID, fingerprint, or passcode check. The signature covers the exact photo plus the time and place, and any edit breaks verification.
CHO HOUSEHOLD
New words in 42s
Rotates every 60 seconds, generated on this phone
Your Halden Park adviser asked for a Proofie™ to confirm a request.
Take a live selfie. Your passkey signs it after Face ID, fingerprint, or passcode.
Take Proofie™Face ID unlocked the key
Fingerprint watermark

Proofie™
HPx4…k2Qd
Verified by Halden Park
Swipe for the next screen
Inside your approvals
When a client asks to move money, the three live words appear on the request in the firm’s view. Your adviser asks one question, confirms the match, and the request goes to your second approver with the check recorded, before anything reaches the custodian.
Nothing replaces your callback, your dual approval or your custodian’s own checks. The second approver sees the request was verified before they sign off, and when your policy calls for it, your adviser requests a Proofie™ from the same screen.
#4127 · $385,000 · Scottsdale condo closing
Henry Cho (phone) · Account: Cho joint brokerage
Ask: What are the words?
Marcus: What are the words?
Henry: Cobalt Lantern Orion.
Security you can verify
Each box below links to its source or to a review with us, so your team can test what we say.
Why it works
Not us, not your IT team, and not a hacker who breaks into our servers. Only the client’s phone and an adviser device your firm has enrolled ever see the real words.
Client’s phone
Sees the live words
Sealed enclave
Hardware-sealed. No one can log in, look inside or change the code.
Key vault
Opens only for the approved code
Code fingerprint match
Enrolled adviser device
Sees the live words
Locked out: can’t read or forge the words
The words are created and unlocked only inside a hardware-sealed compartment in the cloud, called an enclave. Nobody can log into it, look inside or change what runs there, including us.
The encryption key lives in the cloud provider’s key vault, and it opens only for that sealed box running the exact version of the code that was published. If anyone changes a single line, the key stops working.
Our own engineering account is explicitly blocked from decrypting anything. We can deploy and run the system, but we can’t read or forge the words. Even a rogue employee or a breach of our servers gets nothing usable.
Your advisers can see a client’s words only on a device your firm has enrolled with hardware-backed keys. A stolen password alone isn’t enough.
Staff enrollment is signed with a key your firm holds, and it needs more than one person to approve it. We can’t quietly add a staff member.
Your security team can rebuild the software themselves and confirm it produces the exact same fingerprint the key is tied to. They can verify it without relying on us.
Designed so that no one in the middle, including us, can read or forge the words, and you can verify that yourself.
This design is covered by U.S. and international patent applications, filed and pending.
Each device generates three codewords per group locally. They rotate every 60 seconds and work offline.
Read the privacy policyA patent-pending live selfie, signed by the client’s passkey after a Face ID, fingerprint, or passcode check. The signature covers the exact photo plus the time and place; any edit breaks verification.
Visit proofoflife.ioIt works alongside callbacks, dual approval and your custodian’s checks.
Book a security reviewBring your CCO and IT provider; we answer every question.
Book a security reviewEach group key sits in a secure enclave on the deployment server and on each client’s phone. Your team sees the words, never the key.
Book a security reviewEach client’s passkey is bound to their phone. Our server stores only the public key, never the private key.
Book a security reviewThe signature includes a recent public block hash, a value no one could know in advance, which shows the photo was taken after that moment. Nothing is written to a blockchain.
Read our privacy policy and terms.
For your clients
Clients get a verification app in your firm’s name, published under your own App Store and Google Play accounts. We build, submit, and maintain it.

When you call us, three words confirm it’s you. When we call you, ask us for them.
Get startedEveryone in this group sees the same three words.
Swipe for the next screen
Dear Henry and Susan,
When you call us about a transfer, a withdrawal or a change to your accounts, we will now ask one question: “What are the words?” The answer is in Halden Park ID Verify, our app for your phone, which shows three words that change every 60 seconds.
It works the other way, too. When someone calls you from Halden Park, ask them for the words. If they can’t give them, hang up and call us on the number you know.
This adds to the safeguards you already know. Our callbacks, our approvals and your custodian’s protections all stay in place.
Warm regards,
Marcus Bell, CFP
Founder, Halden Park Advisors
Scales with the risk
Your verification policy sets the thresholds, and we help your CCO write it. Your adviser escalates to a Proofie™ when a threshold or trigger applies.
Set by your verification policy
The three words, on every call your policy treats as routine.
When all apply
Three words
Set by your verification policy
The three words and a Proofie™, whenever your policy’s triggers apply or anything feels off.
When any applies
Three words + Proofie™
The return
8 in 10 RIAs call wire fraud and social engineering a major risk 71% of funds transfer fraud insurance claims began with social engineering (Coalition, 2025 claims) $100,000 a typical social engineering sublimit, less than many single client wires
Sources: Golsan Scruggs 2025 Risk Survey; Omega Systems, 2025 Financial Services Cyber Resilience Report.
Questions
Your firm and the client share three words that rotate every 60 seconds in an app branded as your firm. When the client calls, your adviser asks “What are the words?” and checks the answer before acting. A voice clone can copy how the client sounds, but not the three words on their phone.
No product satisfies a rule on its own. Trust Onion supports the written verification procedures those rules expect, and your adviser’s check appears on the request your second approver signs. Your CCO decides how it fits your policies.
Because the number can be moved. A SIM swap, a port-out or call forwarding sends your callback to the attacker. The three words are generated on the client’s phone and still hold when that happens. Your callback stays in place.
No. Your custodian keeps its own checks. The three words come first, before your team sends any instruction to the custodian.
Often only in part. Social engineering coverage usually comes as an extension with a sublimit, often around $100,000, and some policies ask you to show you verified the request before a claim pays. Ask your carrier how a written verification procedure fits your policy.
Your adviser sets it up with them in a review meeting, and the app opens ready, with your firm already in the group. After that, they answer one question. Family members can join the household group to help.
Your team sees the current words, never the key. Each group key sits in a secure enclave on the deployment server and on each client’s phone. Proofies™ are private by default for family offices. A Proofie™ your team requests is shared with your office and no one else.
Your firm’s. The app carries your firm’s name and logo, published under your own App Store and Google Play accounts.
Next step
Send this page to your CCO and your IT provider, then book a review with us before you decide.
Your team can test how the three words and Proofies™ work, and where your callbacks, dual approval and custodian checks fit.
“Before anything goes to the custodian: what are the words?”